Technowand
M365 Secure Score

Back to Secure Score Hub

How to Disable Administrator Account Enumeration on Elevation

Last updated: November 2026

When a Windows device prompts for elevated privileges, it can expose administrator account names — giving attackers a free list of high-value targets. This guide walks you through disabling administrator account enumeration on elevation, a quick win that improves your Microsoft 365 Secure Score and reduces attacker reconnaissance opportunities.

Estimated time: 15 minutes. Requires Global Administrator or Intune Administrator access and Windows devices enrolled in Intune.

What You'll Achieve

Reduce Account Enumeration RiskPrevent attackers or malware on a compromised endpoint from harvesting administrator account names via UAC elevation prompts.
Improve Your Secure ScoreThis control is tracked by Microsoft Secure Score. Completing it gives your organisation measurable, auditable security progress.
Enforce Least PrivilegeHiding admin account names on elevation reinforces least-privilege discipline and makes lateral movement harder for attackers.

Why This Matters

By default, when a user triggers a UAC elevation prompt on Windows, the system displays administrator account names in the credentials dialog. This behaviour allows anyone with physical or remote access to a machine — including malware — to enumerate privileged account names without any authentication. In a targeted attack or ransomware scenario, this reconnaissance step can significantly accelerate lateral movement.

Disabling this enumeration removes a low-effort data source for attackers and is a recommended control under Microsoft's own security baseline. It is one of the faster Secure Score wins available — no licensing upgrade required, and it can be deployed fleet-wide via Intune or Group Policy.

Microsoft flags this as a Secure Score improvement action for all tenants where the control is not yet enforced.
Before You Start

You will need: Global Administrator or Security Administrator role in Microsoft 365; access to Microsoft Intune (preferred) or on-premises Group Policy management; and a change window if deploying to production endpoints.

Step-by-Step Instructions

Follow these five steps to create and deploy the policy in Microsoft Intune. The screenshots come from a real deployment by our engineers.

1

Sign in and confirm your admin role

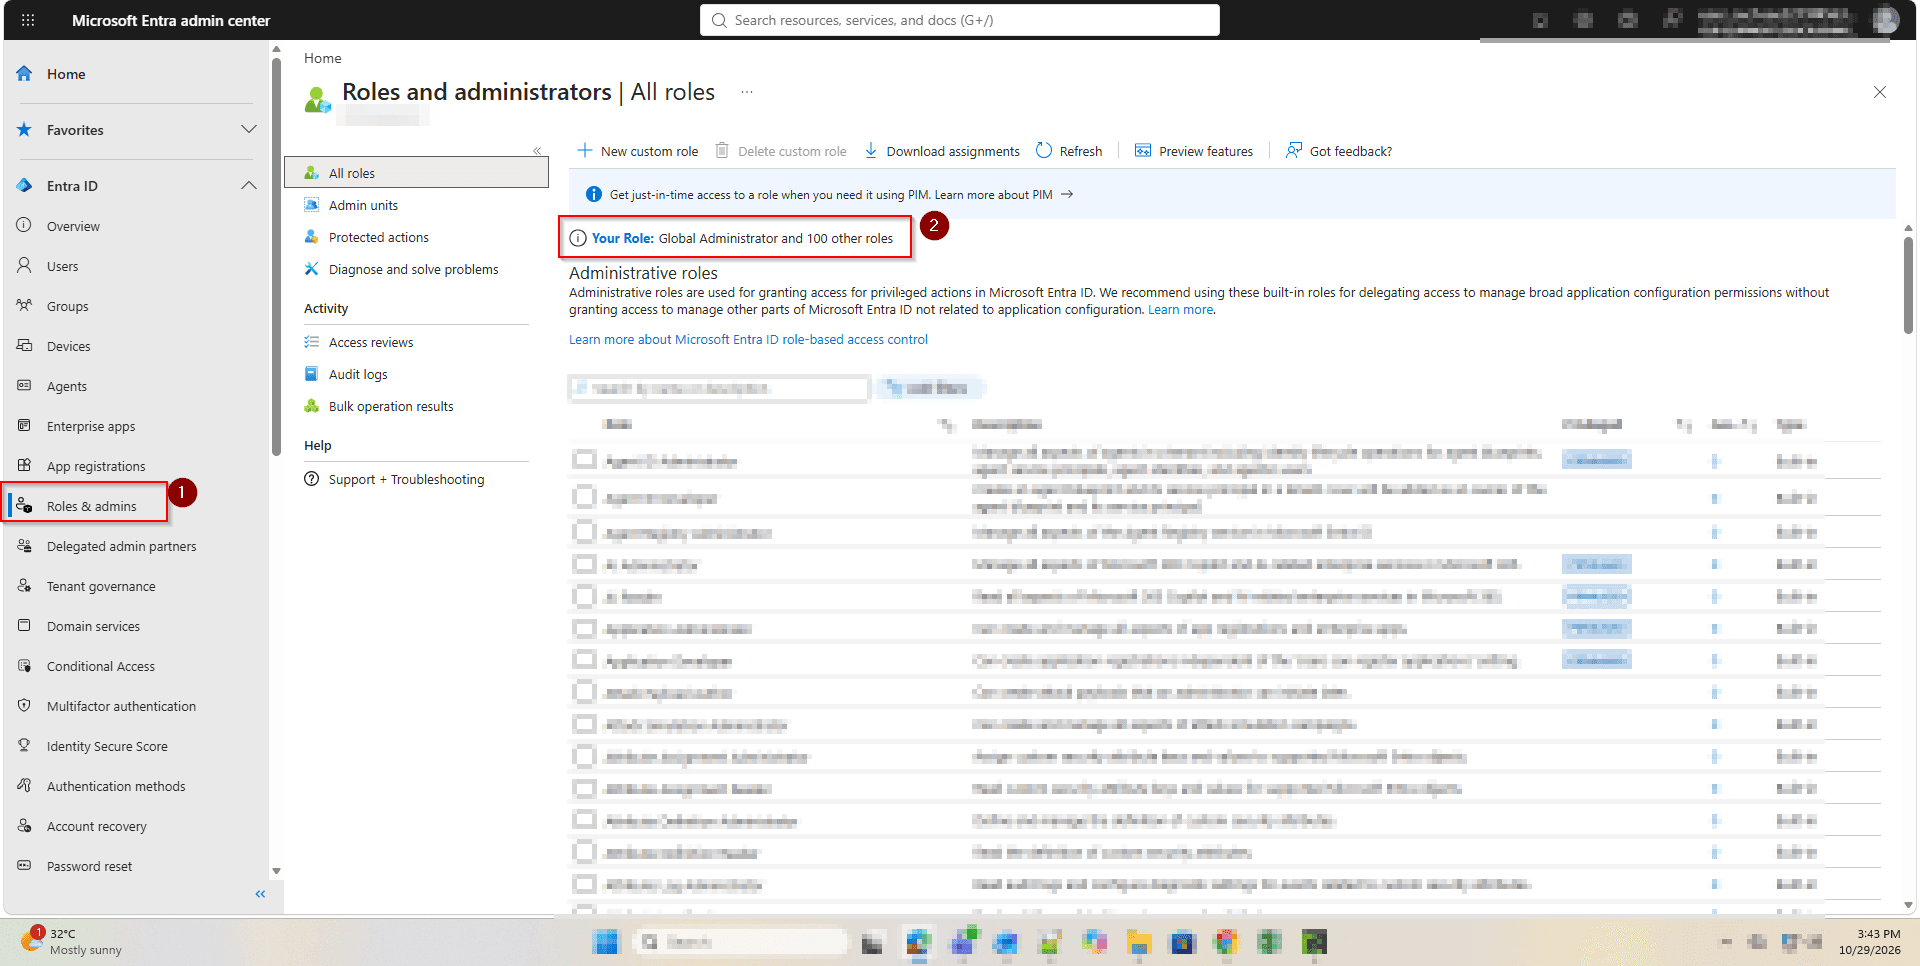
Go to entra.microsoft.com and sign in. Open Roles & admins and check that Your Role shows Global Administrator or Intune Administrator. Confirm you are in the correct tenant before you continue.

Sign in and confirm your admin role
2

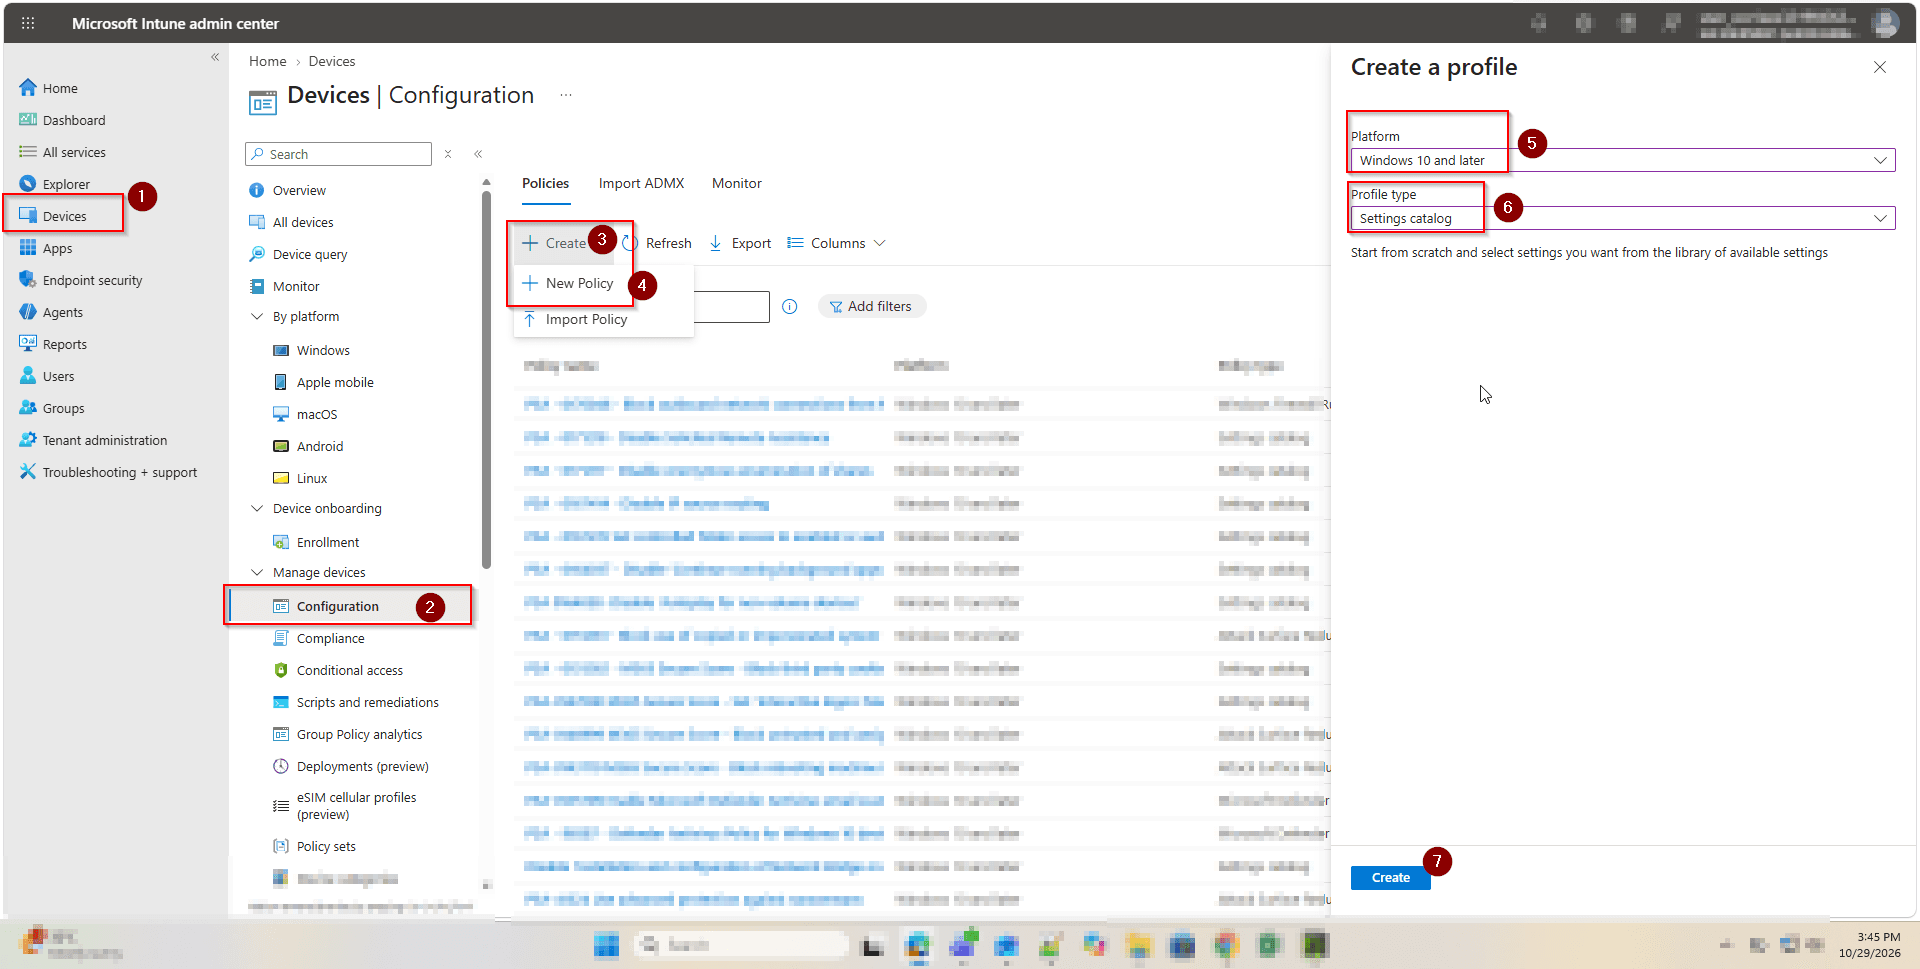
Create a settings catalog profile in Intune

Go to intune.microsoft.com and select Devices, then Configuration. Click Create, then New Policy. Set Platform to Windows 10 and later and Profile type to Settings catalog, then click Create. Note: this setting is not offered under Endpoint security > Account protection, so use the settings catalog.

Create a settings catalog profile in Intune
3

Name the policy

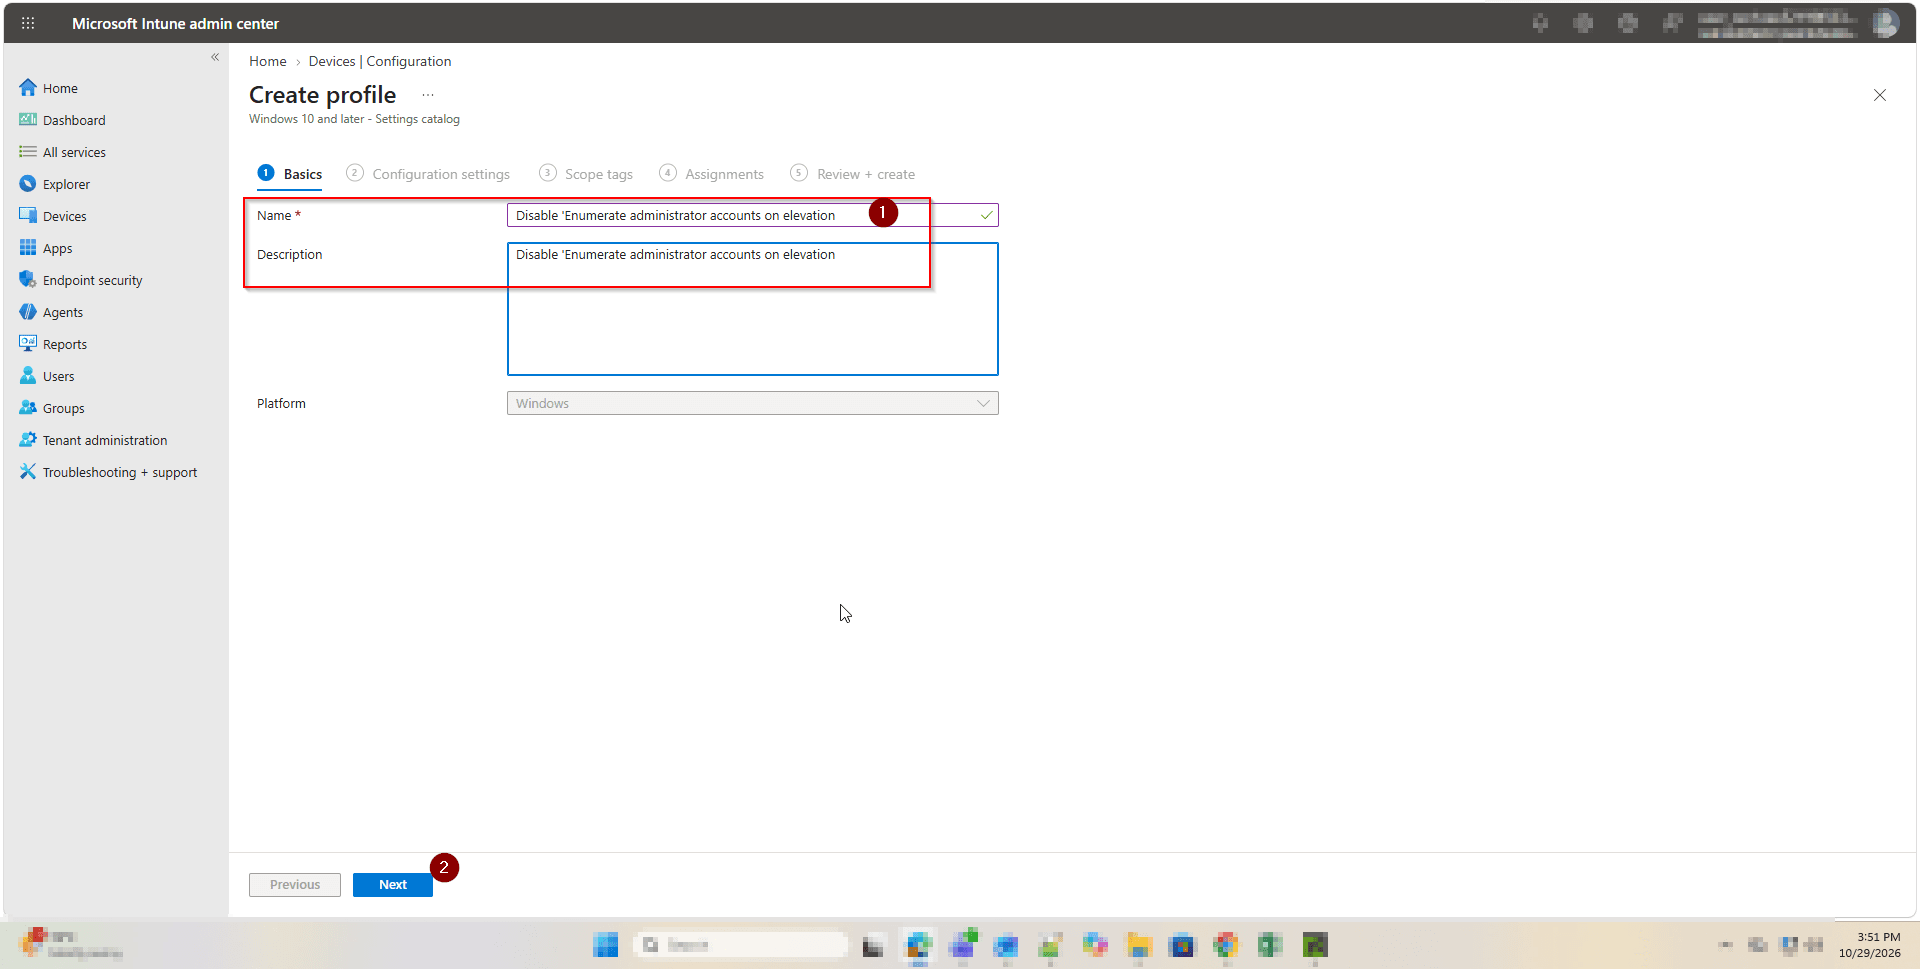
On the Basics tab, enter a clear name and description such as 'Disable Enumerate administrator accounts on elevation', then click Next.

Name the policy
4

Set 'Enumerate administrator accounts on elevation' to Disabled

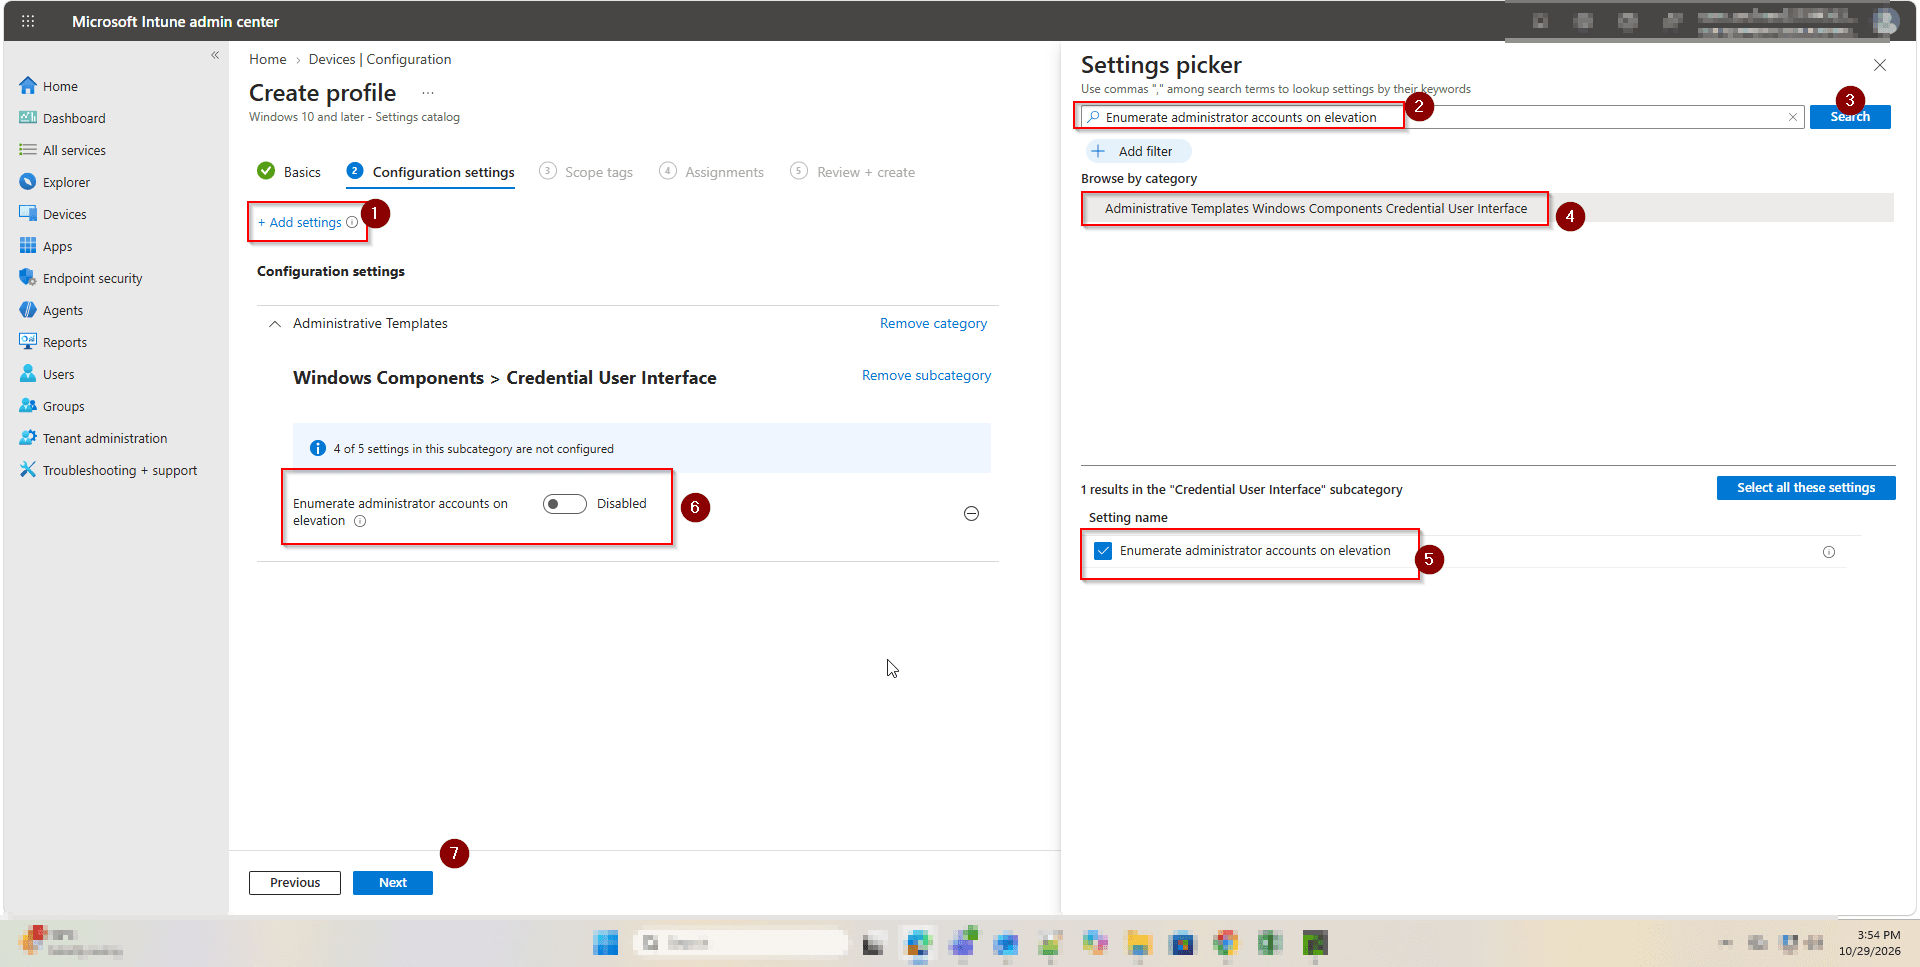
Click Add settings and search for 'Enumerate administrator accounts on elevation'. Select the Administrative Templates > Windows Components > Credential User Interface category, tick the setting, then close the picker. Set the toggle to Disabled. Click Next, assign the policy to your Windows device groups, then Review + create.

Set 'Enumerate administrator accounts on elevation' to Disabled
5

Confirm in Microsoft Secure Score

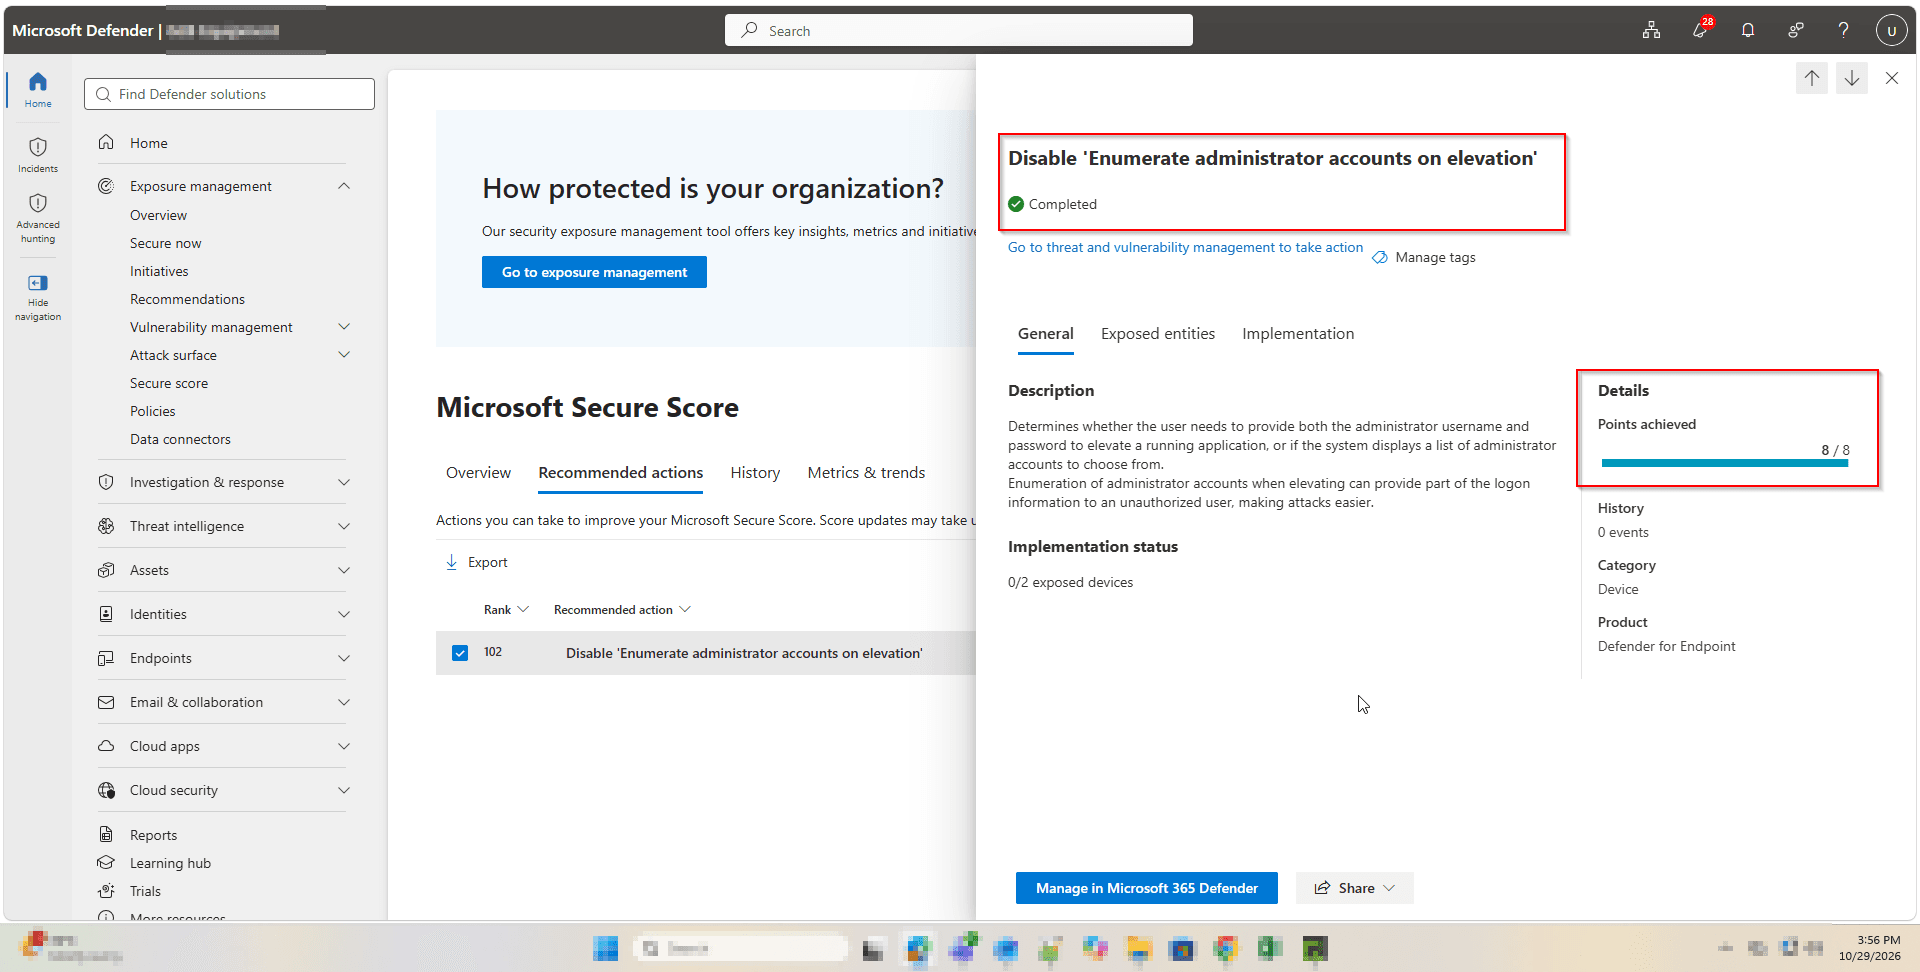
In the Microsoft Defender portal, go to Exposure management > Secure score > Recommended actions and open Disable 'Enumerate administrator accounts on elevation'. Once devices have synced it shows Completed with full points achieved.

Confirm in Microsoft Secure Score

How to Confirm It Worked

  • On a managed Windows device, trigger a UAC elevation prompt — administrator account names should no longer appear in the credentials dialog.
  • In Microsoft Defender (security.microsoft.com > Secure Score > Improvement Actions), the control should show as Completed once policy has propagated.
  • In Intune, check the policy assignment report to confirm the profile has applied successfully to your target device group.
  • Registry check on a test device: HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\CredUI, value EnumerateAdministrators should be 0.
  • Microsoft reference: Policy CSP CredentialsUI, EnumerateAdministrators (Microsoft Learn).

Frequently Asked Questions

What is administrator account enumeration on elevation?

When Windows displays a UAC (User Account Control) elevation prompt, it can show a list of administrator account names for the user to choose from. This behaviour is called administrator account enumeration on elevation. While convenient, it allows anyone — including malware — to harvest privileged account names without authenticating.

Will disabling this setting break anything for end users?

No. End users who need to approve elevation prompts will still see the UAC dialog — they just won't be presented with a list of administrator accounts to choose from. They will need to type the administrator username manually. This is standard behaviour on well-configured enterprise systems.

Can I deploy this without Intune?

Yes. For on-premises or hybrid environments, use Group Policy: Computer Configuration > Administrative Templates > Windows Components > Credential User Interface > 'Enumerate administrator accounts on elevation'. Set it to Disabled and link the GPO to the relevant OUs.

How long does it take for the Secure Score to update after applying the policy?

Microsoft Secure Score typically refreshes within 24–48 hours of the policy being detected on enrolled devices. Intune policy propagation itself usually completes within a few hours depending on device check-in intervals.

Does this control apply to Azure AD joined devices as well as on-premises machines?

Yes. When deployed as an Intune settings catalog profile, it applies to Entra joined and hybrid joined Windows devices enrolled in Intune. For on-premises AD-joined devices not enrolled in Intune, use Group Policy.

Want Us to Handle Your Secure Score Improvements?

Technowand's Microsoft 365 security specialists can assess your current Secure Score, prioritise the highest-impact controls, and deploy them across your tenant — so your team can focus on the business.